Design reliable cloud infrastructures across multiple Italian Regions
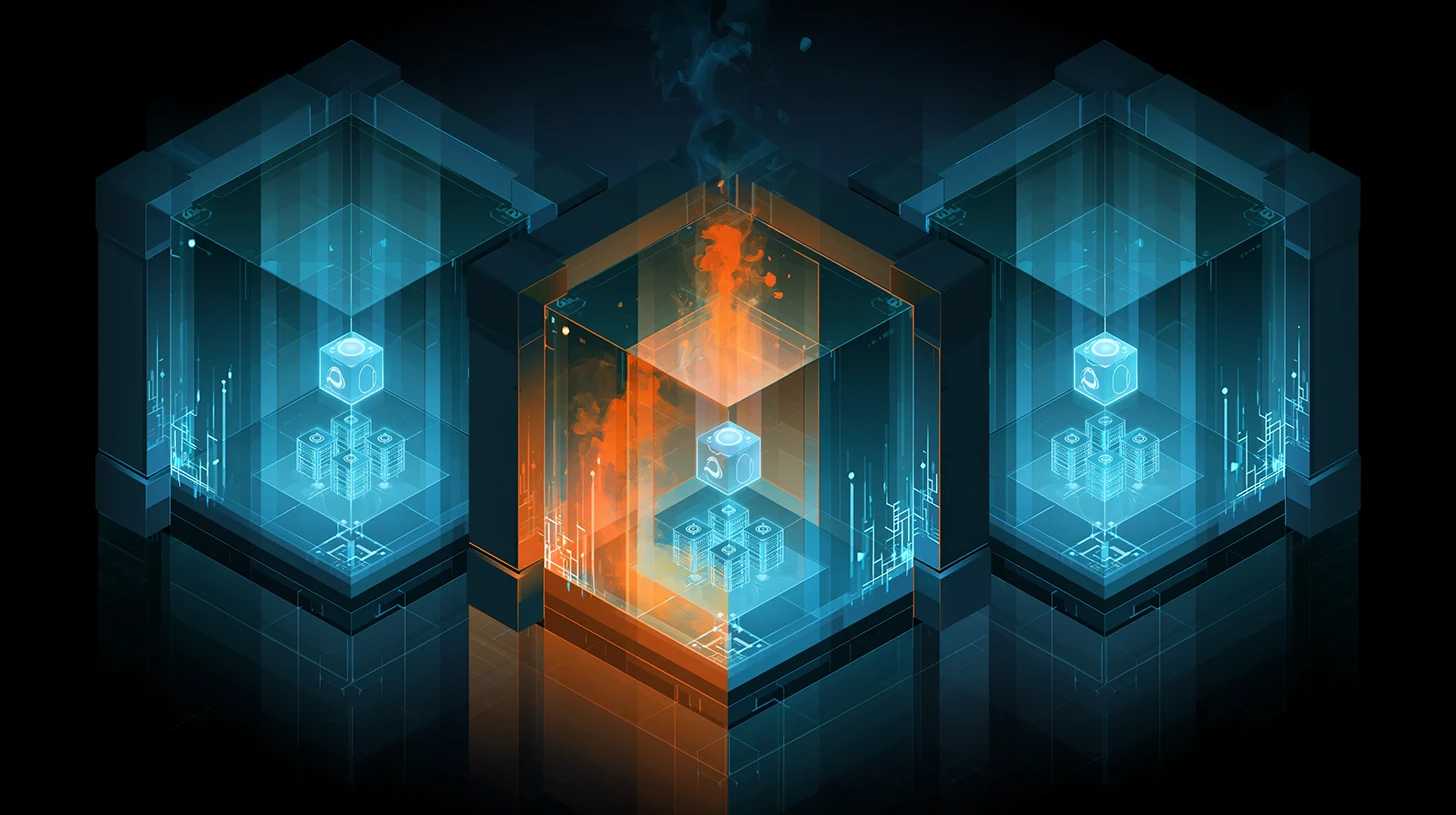
Eliminate Single Points of Failure with an infrastructure featuring three Italian Regions, ideal for segregating your mission-critical workloads.
True resilience requires isolating your IaaS control planes
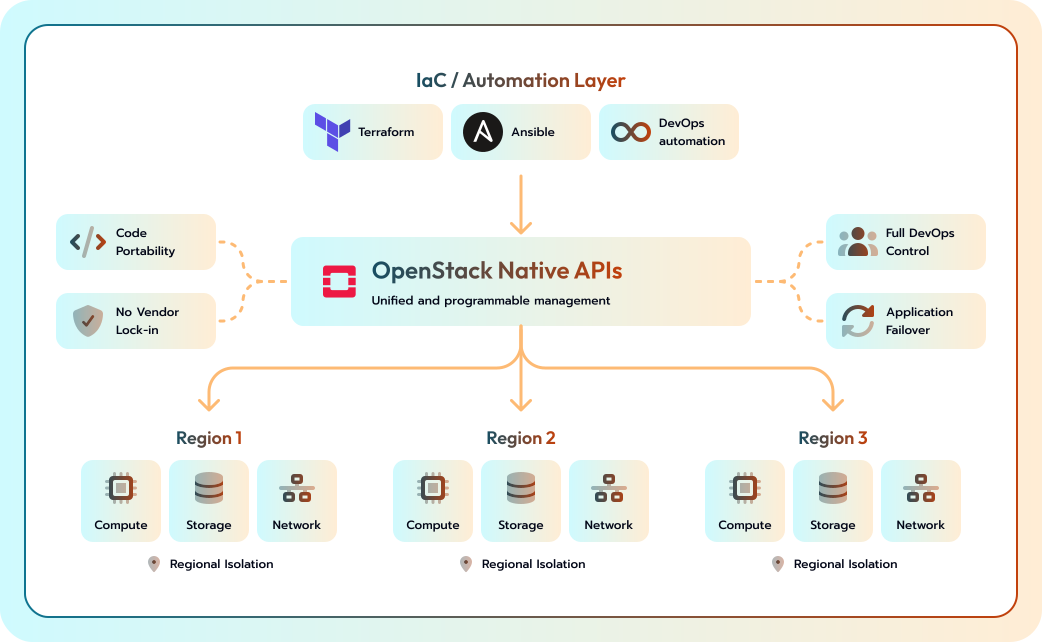
The domino effect caused by a logical or software error propagating through shared networks and orchestration layers should not be a limitation. Thanks to a distributed infrastructure across three fully independent Italian regions in terms of network configurations and computational resources you gain true business continuity with absolute control over replication, routing, and isolation logic, ensuring genuine Business Continuity.
Overcome the structural and economic limitations of conventional geo-distributed clouds
Unpredictable replication traffic costs
Data synchronization between different Regions on hyperscalers typically incurs asymmetric and complex network fees. Total costs escalate exponentially, turning Disaster Recovery into a financial barrier for businesses.
Rischio di blackout globale dei tuoi servizi
Multi-region architectures of large providers often share the same logical authentication or DNS systems. A single central software bug or administrative block propagates instantly to all nodes, nullifying the physical isolation of data centers.
Proprietary network stack lock-in
High reliability on general-purpose clouds necessitates the use of proprietary routing and load balancing services. This eliminates Layer 2 traffic visibility and prevents infrastructure portability, locking the application to a single vendor.
Choose a cloud architecture for Disaster Recovery without compromise
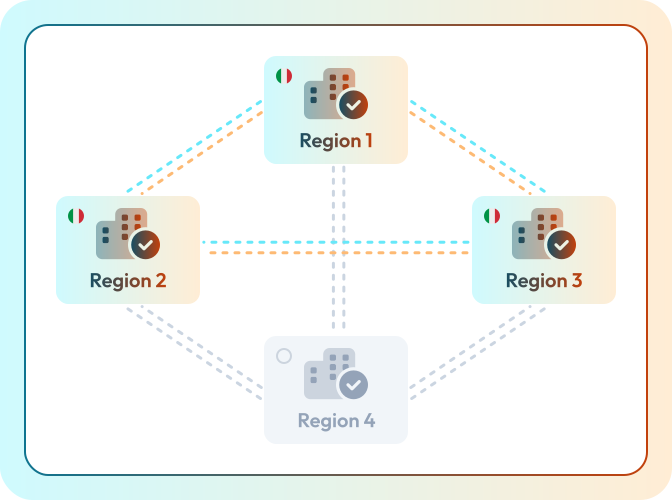
Three zones of real hardware and logical isolation in Italy
Each CloudFire region is a fully autonomous Fault Domain, without shared authentication databases or centralized orchestration systems. By distributing workloads across distinct regions, you achieve true segregation: any outage on one node cannot propagate to other environments.
Absolute financial predictability with zero egress fees on internet bandwidth
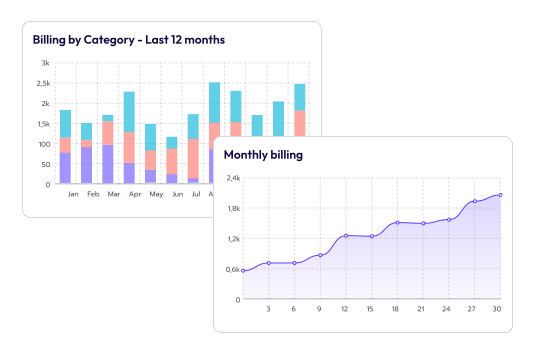
Synchronize your databases and enable continuous replication leveraging stable, direct connections. CloudFire completely eliminates traffic egress costs (egress fees) to the internet, allowing you to calculate the TCO of your Business Continuity plan with linear precision and no volume-based billing surprises.
Standardized automation via native OpenStack APIs
Manage isolated infrastructure uniformly and programmatically with Infrastructure as Code (IaC). Leverage native OpenStack API access to manage compute, storage, and networks across all Regions via Terraform and Ansible, eliminating vendor lock-in and giving your team total control over failover processes.
Resources
Cloud privacy isn't enough without access control. Discover how digital sovereignty ensures you maintain real control over your data.

S3 Scalable Object Storage
Archivia i tuoi dati in uno spazio Ceph Based scalabile e sicuro, S3 compatibile e senza sorprese nei costi.

Openstack as a Service
Governa e distribuisci in autonomia risorse cloud in Italia in modalità as a Service.
FAQ
How is true logical isolation between CloudFire regions guaranteed?
Each of our regions (including the new RM1 region) is designed as a fully independent Fault Domain. This means the Control Plane, the Keystone authentication databases, and the OpenStack orchestration systems are physically and logically separated for each geographic area. An outage or software bug in one region cannot in any way propagate to or compromise the stability and reachability of the others.
Does 'Zero Egress Fees' apply both to traffic between regions and to outbound traffic?
Yes. CloudFire completely eliminates egress fees in every direction: both for data flows exchanged between our regions (e.g., synchronous database replication or storage clusters) and for traffic to the public internet. You pay only for compute resources and allocated bandwidth, giving you a linear, predictable Disaster Recovery TCO with no variations based on consumed volumes.