
Cloud Infrastructure with OpenStack for MSPs and System Integrators
Manage your clients' workloads with maximum control over resources, predictable costs, and the compliance of a sovereign cloud based in Italy.
Behind every managed service lies a challenge of governance and profitability that MSPs and System Integrators know well. CloudFire has developed Openstack as a Service to eliminate friction between technical design and economic sustainability. With our CloudFire IaaS service, you integrate aSelf-service cloud infrastructure that speaks your language, designed for those committed to meeting client SLAs.
How CloudFire beats the hidden pitfalls of generic cloud platforms
Cost transparency to help you grow
No more unpredictable invoices due to data traffic and micro-transactions that only erode your operating margin.
Personalized and expert support
Receive expert, responsive support for every need. In critical situations, standardized support simply cannot replace a direct engineering contact.
Complete networking freedom
Proprietary lock-in risk and the difficulty of configuring complex network topologies should not limit the freedom to evolve your services.
Unlock more value for your services with a scalable cloud infrastructure and granular control
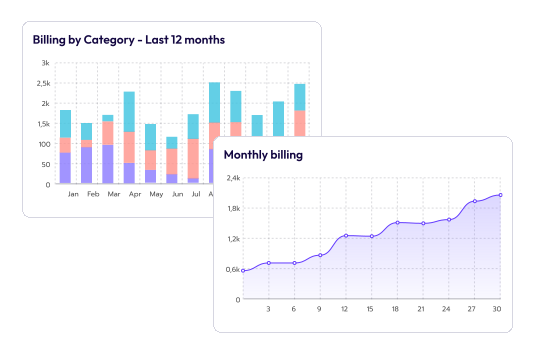
Fixed and transparent margin
Our IaaS services pricing is based on the allocated resources, with no hidden costs. You always know how much you spend and how much you earn.
No-lock-in cloud architecture
Leverage the open global standard of Openstack. Your freedom of migration and integration is guaranteed by open source code.
Business Critical IaaS Performance per Workload
Get the guaranteed resources you need, without noisy neighbor incidents and with minimal latency for applications that cannot afford slowdowns.
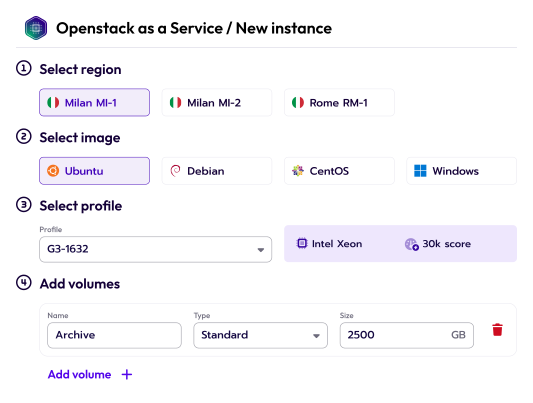
Self-manage IaaS for your clients
Multi-tenant client management
Automation and Integration
Advanced Networking

Data Sovereignty and Multi-Region Resilience for Public Administrations
We operate with certified Data Centers, all located in Italy. The qualification ACN and the regulatory compliance allow you to confidently approach even the most regulated sectors and Public Administration.
Discover CloudFire Infrastructure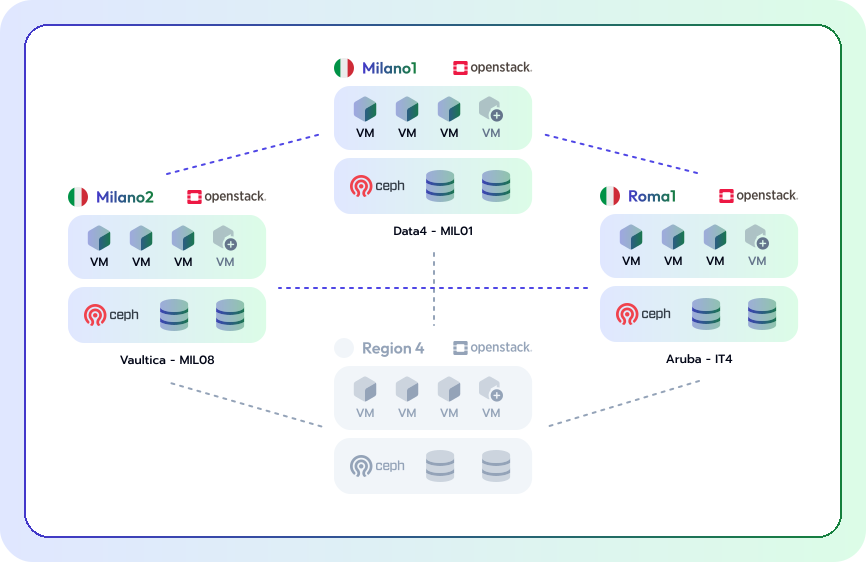
Resources
Cloud privacy isn't enough without access control. Discover how digital sovereignty ensures you maintain real control over your data.

S3 Scalable Object Storage
Archivia i tuoi dati in uno spazio Ceph Based scalabile e sicuro, S3 compatibile e senza sorprese nei costi.

Openstack as a Service
Governa e distribuisci in autonomia risorse cloud in Italia in modalità as a Service.
FAQ
Does CloudFire offer support for migrating my customers' workloads?
Yes. We know migration is a critical phase for an MSP. In addition to technical documentation, our team of Solution Architects provides engineering support to help you plan and move workloads (on-prem or from other clouds) to CloudFire's OpenStack infrastructure, keeping downtime to a minimum.
Can I manage billing and resources for each customer separately?
Absolutely. With CloudFire Console, you can create and manage separate Tenants for each of your customers. This gives you complete operational segregation and clear visibility into each project's consumption, making it easier to pass through costs and manage your margins.
Is the infrastructure compatible with Terraform or other Infrastructure as Code (IaC) tools?
Yes. Because we are built on native OpenStack standards, we guarantee full API access. You can automate resource provisioning, configuration, and management using Terraform, Ansible, or any other tool compatible with the OpenStack ecosystem, giving your customers fast, professional deployments.
Can I use CloudFire for Public Administration (PA) projects?
Yes. CloudFire is an ACN-qualified infrastructure provider (Italy's National Cybersecurity Agency). Data sovereignty is guaranteed because our data centers are located exclusively in Italy. This lets you take part in tenders and projects for the Public Administration (PA) and regulated industries with full regulatory compliance.
What kind of network isolation can I configure for my customers?
Our platform supports advanced Layer 2 segregation. You can configure virtual private networks, VLANs, and granular firewall rules for each tenant. This ensures that one customer's traffic is fully isolated from the others, letting you build complex, secure architectures as if you were in a local data center.
How is technical support handled in critical situations?
Unlike large general-purpose cloud providers, CloudFire offers direct tier 2 and tier 3 technical support. When you need help, you work directly with engineers who know the infrastructure, ensuring fast response times and targeted solutions for your business-critical services.